SITE360.
Read the ground. Map the risk. Close the gap. Hold the line.
Built for venues, crowd events, and public open spaces, by people who have held the duty, not just consulted to it. One framework. Three domains. Four phases. Built to be lived with.
Lead · Anthony Karpanos
TAKE THE FREE SITE VULNERABILITY ASSESSMENT BELOW.
Most site work falls short.
Site security is decided where the place, the people, and the legal duty meet.
Most site work in Australia falls short of that joint. The security consultancy hands over a sixty-page report and walks. The WHS consultancy stops at the back-of-house door. Neither closes the gap between physical risk, operational reality, and the duty the operator carries.
SITE360 closes it.
The framework runs the standard risk management process, Identify, Assess, Control, Review, anchored in AS/NZS ISO 31000:2018 and the Safe Work Australia How to manage work health and safety risks Code of Practice. It is delivered against the harmonised Work Health & Safety Acts and Regulations, the ANZCTC crowded places framework, and CPTED principles across first and second generation.
And it is delivered by operators who have run high-risk venues at scale, run major fixtures from inside the duty-holder seat, and held safety responsibility across crowded ground in stadium, sport, motorsport, athletics, and civic environments.
One framework. Three domains. Four phases.
A single discipline, applied across three operating contexts, in four ordered steps. Built to be lived with, not filed and forgotten.
One framework
A single discipline, SITE360, anchored in AS/NZS ISO 31000:2018 and the Safe Work Australia Code of Practice. The same logic, every site.
Three domains
Venues. Events. Public Realm. Each with its own threat profile, vulnerability surface, and CPTED weight.
Four phases
Identify, Assess, Control, Review. The standard risk management process, in language regulators trust.
Three domains.
One framework, three operating contexts. Each domain has its own threat profile, vulnerability surface, and CPTED weight, but the discipline is the same.
SITE360 | Venues
Perimeter · Concourse · Bowl
For fixed assets with a continuous operating tempo. Stadiums, arenas, sports centres, training facilities, multi-tenant complexes, civic and cultural buildings, transport interchanges. Assessment runs across the full operating cycle, and across three concentric rings. Designed to live alongside the venue's safety management system, not parallel to it.
SITE360 | Events
Bump-in · Show · Bump-out
For time-bounded operations that bring crowds, infrastructure, and command structure to a place. Music festivals, sporting fixtures, public ceremonies, corporate activations, regional events, government and state visits. Assessment spans the full operating cycle and integrates the ANZCTC crowded places framework, crowd density modelling, hostile vehicle mitigation, and command-and-control architecture.
SITE360 | Public Realm
Place · Movement · Activity
For public open spaces and the soft urban edge. Town centres, transit precincts, foreshores, plazas, parks, and the public-facing fronts of mixed-use developments. Built around CPTED principles across both first and second generation. The work that sits upstream of every venue and every event.
Four phases.
The standard risk management process, in language regulators trust, delivered by operators who have held the duty.
Identify
Read the ground.Establish context. Walk the site. Build a current threat picture across natural, accidental, deliberate, and crowd-dynamic categories. Define the duty: owner, occupier, operator, event organiser, PCBU.
Aligned toISO 31000:2018 § 5-6.3 · WHS Code of Practice Step 1 · WHS Act Part 2 Div 2 (harmonised)
Assess
Map the risk.Vulnerability assessment scenario by scenario, walked on the ground. CPTED audit across the five first-generation principles, with second-generation overlay where the user dynamic warrants it. Risk analysis on a 5×5 matrix tested against the operator's risk appetite.
Aligned toISO 31000:2018 § 6.4 · WHS Code of Practice Step 2 · HB 167:2006
Control
Close the gap.Each recommendation tied to a specific vulnerability and a specific consequence avoided, with indicative cost and a delivery sequence. Capital separated from operational. Immediate separated from long-term. HVM specifications calibrated to expected vehicle weight and street-network speed.
Aligned toISO 31000:2018 § 6.5 · WHS Code of Practice Step 3 · WHS Regulations reg 36 (harmonised)
Review
Hold the line.Monitoring and review regime. Maintenance and management plan that protects the design intent against the next operational cycle. Review cadence and reassessment triggers defined: incident, refurbishment, change of use, change in threat profile, change in user dynamic.
Aligned toISO 31000:2018 § 6.6 · WHS Code of Practice Step 4 · AS 3745
What you receive.
A complete evidence package built to defend the operator's duty, and to be put to work the day it lands.
Threat & Context Register
The current threat picture, mapped to the duty and the operating tempo.
Vulnerability Assessment
Scenario by scenario, walked on the ground, not desk-built.
CPTED Audit
First and second generation, applied where the user dynamic warrants it.
Risk Register
5×5 matrix. Current control effectiveness. Residual rating. Tested against appetite.
Treatment Plan
Capital separated from operational. Immediate separated from long-term. Costed.
Crowded Places Assessment
Where density profile triggers it. Aligned to the ANZCTC framework.
Management & Review Regime
The plan that protects the design intent across the next operational cycle.
Executive Briefing
Walked through with the duty-holder. Not handed over and forgotten.
Held the duty. Not just consulted to it.
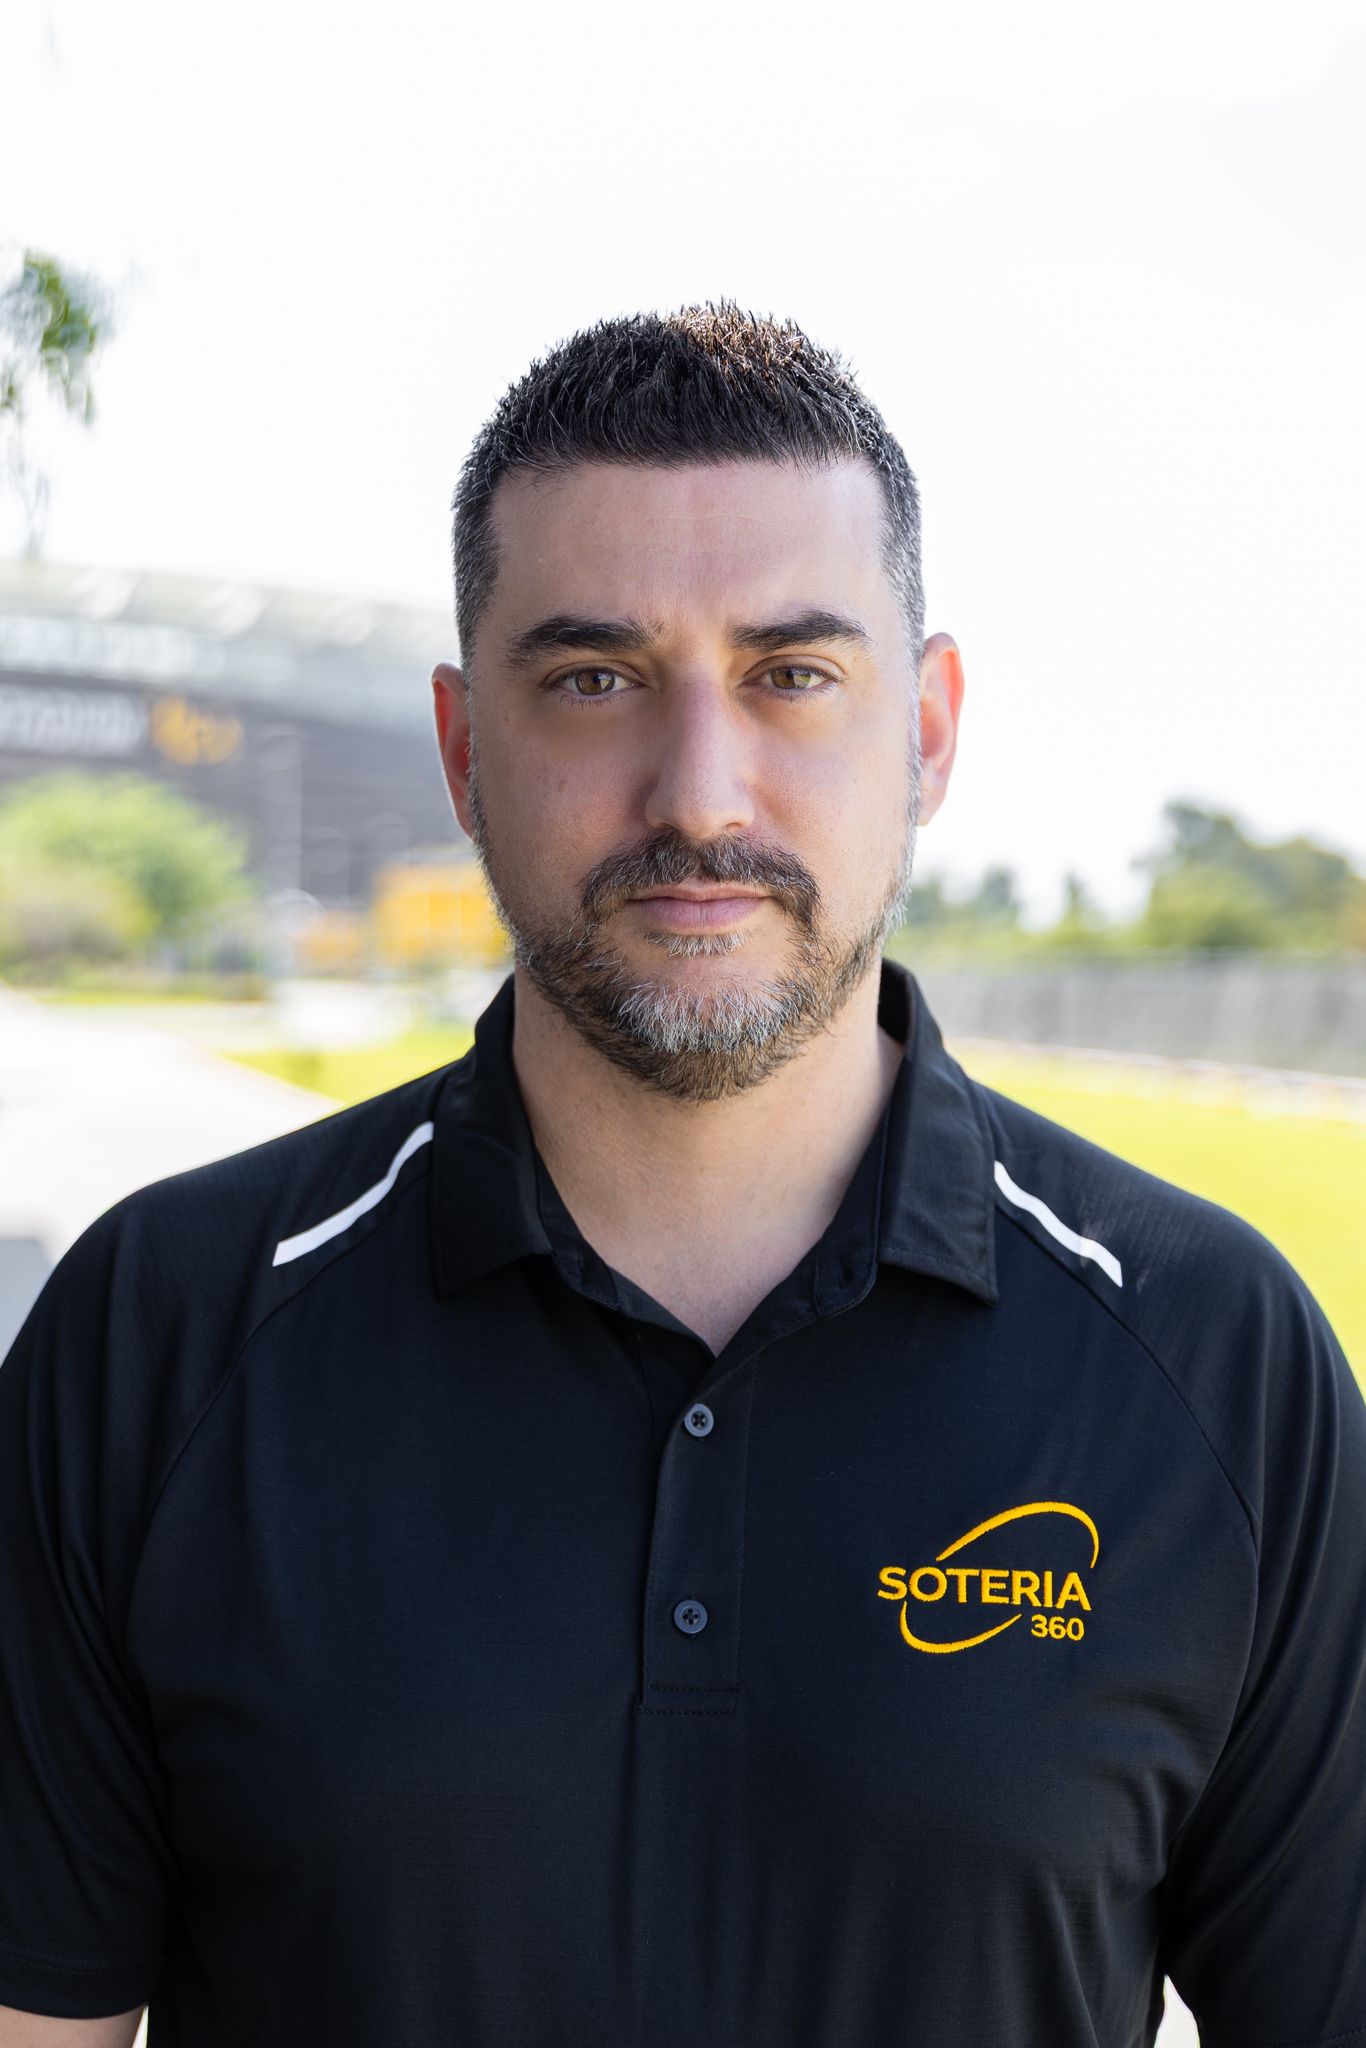
Anthony Karpanos
SITE360 is led by Anthony Karpanos. He has run safety and risk across a stadium and venue portfolio at scale, sitting in the duty-holder seat, not adjacent to it. That experience is the difference between a report you file and a framework you live with.
Engagement Director Josh Smith oversees framework delivery, scope governance, and reporting standards across every SITE360 engagement.
- Former Chief Safety & Risk Officer, VenuesWest
- Safety oversight across 14 venues, $3.3B asset value
- 6.24 million annual patronage across the portfolio
- WorkSafe WA Platinum Certificate of Achievement
- ICAM Lead Investigator
- Stadium · sport · motorsport · athletics · civic environments
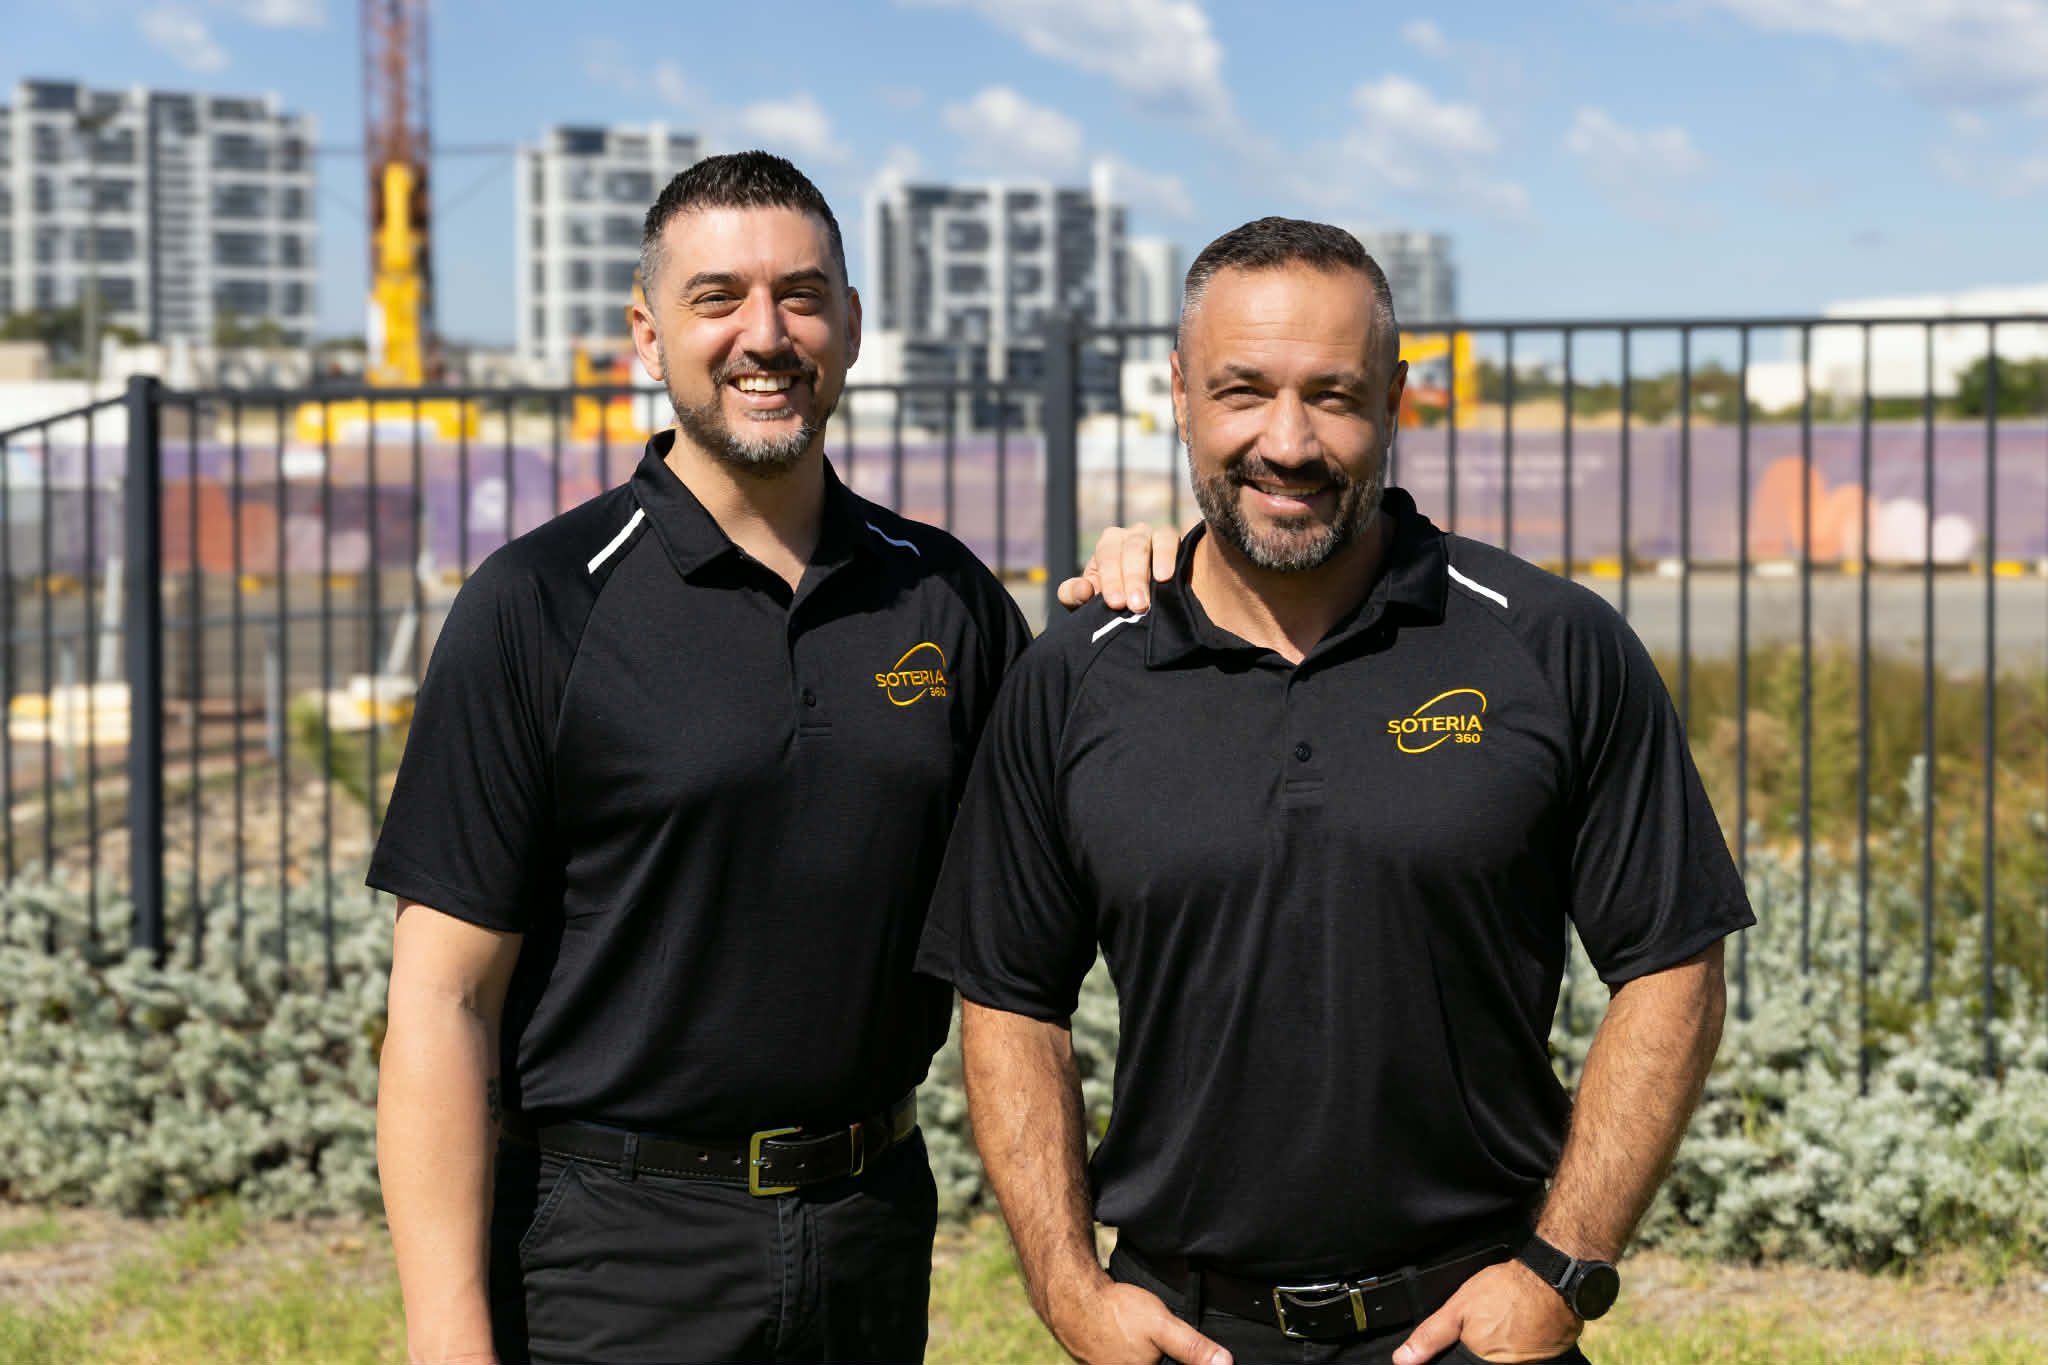
The team behind the framework · Anthony Karpanos · Josh Smith · Soteria 360
Anchored where it counts.
SITE360 is delivered against the standards regulators, insurers, and counsel actually rely on. No private frameworks. No vendor-built ratings.
ISO 31000:2018
Risk Management, Guidelines
HB 167:2006
Security Risk Management
WHS Act
Australian Harmonised Framework
WHS Regs
Australian Harmonised Framework
Code of Practice
How to Manage WHS Risks
ANZCTC
Crowded Places Framework
CPTED 1&2
First & Second Generation
AS/NZS 1158
Lighting Standards
AS 3745
Emergency Planning
Standards are listed in every report's provenance statement, and every recommendation traces back to a specific clause. The framework is auditable end to end.
Start here.
Three ways in. Start where you are, and we will meet you on the ground.
Book a call
30 minutes. Talk through your site, your event, or your obligation. No deck. No pitch.
Book → 02Download the capability statement
The full SITE360 framework as a PDF. Standards anchor, phases, domains, deliverables.
Download ↓ 03Send an enquiry
A site, an event, a regulatory trigger, or a brief you are still shaping. Tell us what you are working with.
Enquire →Protecting People · Powering WorkforcesSoteria 360 · soteria360.com.au